
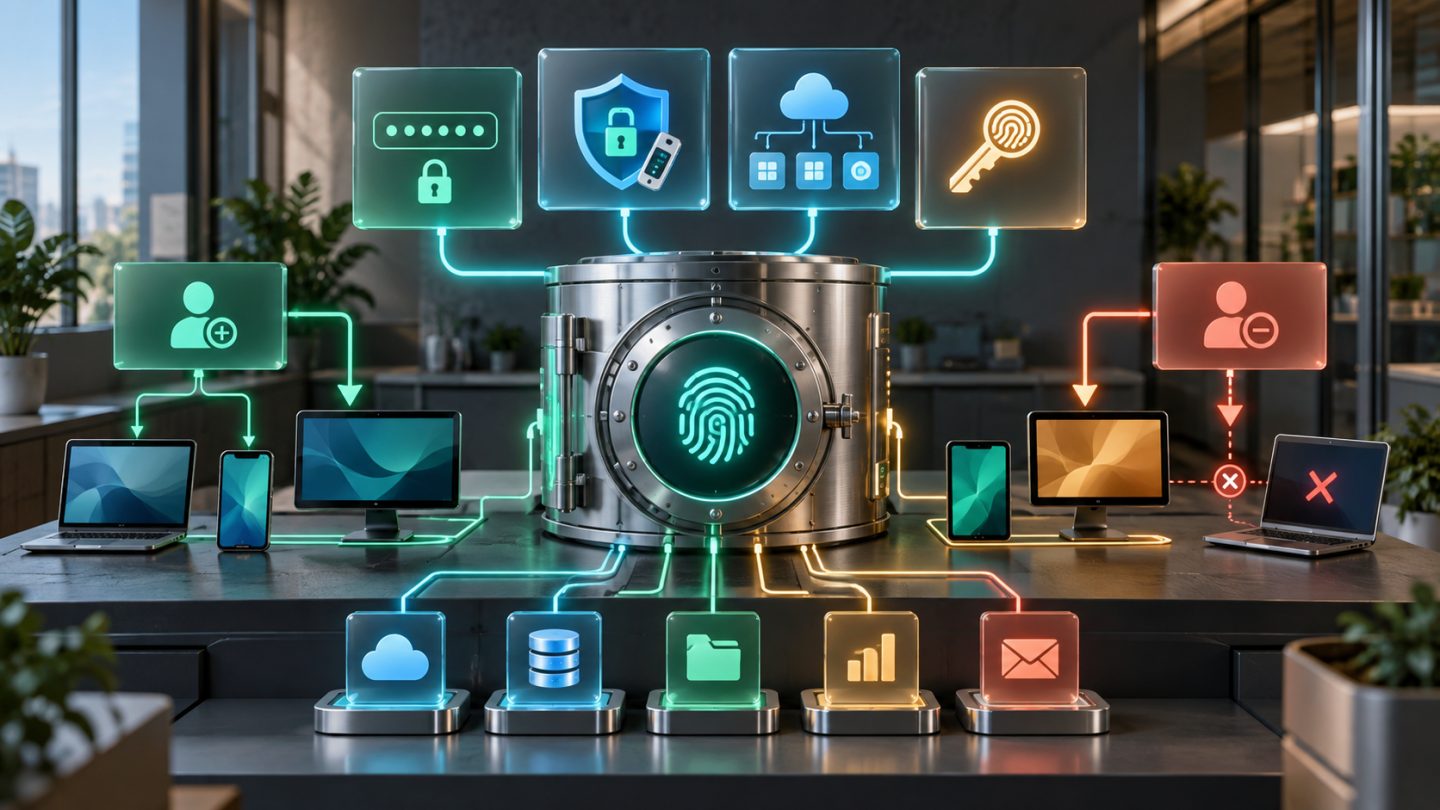
Employees change departments but retain old folder access. Vendors finish contracts but keep accounts. Temporary administrators remain privileged. Excess access can accumulate even when MFA and strong passwords are in place.
This article proposes a manageable access review with approvers, evidence and post-change checks. It is an operating template, not an instruction to disable accounts in bulk.
1. Review authorization, not just sign-ins
CIS Control 6 covers granting, managing and revoking privileges for user, administrator and service accounts. The review question is whether current access remains necessary for current work.
MFA strengthens authentication; it does not decide whether someone needs to export the entire customer database. Frequent sign-ins do not justify every attached permission.
2. Start with one important system
Choose a scope such as the CRM or document repository, record the snapshot time and name its owner. Avoid collecting every enterprise account before identifying who can judge each system's business needs.
| Review field | Purpose |
|---|---|
| Account and person/service owner | Establish responsibility |
| Effective rights and grant source | Distinguish direct, group and inherited access |
| Business reason | Check current need |
| Approver and expiry | Control temporary access and exceptions |
| Decision and execution evidence | Track approval through completion |
Exclude passwords, secrets and tokens. Permission inventories are sensitive too; share them only with review participants.
3. Prioritize high-impact privileges
Start with administration, data export, payment changes, public sharing and third-party access. Compare departures, role changes, contract endings and completed projects with actual permissions.
A missing recent sign-in is an investigation signal, not a sufficient revocation rule. Service accounts may operate through APIs or scheduled jobs without human-style sign-in records.
4. Separate decisions from implementation
- The business owner chooses retain, reduce, revoke or investigate.
- Technical staff identify grant sources and affected dependencies.
- An authorized approver confirms the change and timing.
- Execute only the approved scope and retain change evidence.
- Verify effective permissions and legitimate workflows afterward.
Removing a direct grant may leave access through nested groups. Inspect effective rights instead of relying on a success message. Preserve an approved emergency administration path to avoid locking out all administrators.
5. Give exceptions owners and expiry dates
For example, a vendor needs temporary troubleshooting access for a week. Record scope, reason, sponsor, expiry and revocation verification. If a technical dependency prevents reduction, document the risk and remediation plan rather than marking the item complete.
For service accounts, identify the consuming application, owner and approved credential storage. Secret rotation or job changes require coordinated implementation and rollback planning.
6. Measure closed work
- How many rights have a business-owner decision?
- How many revocations are implemented and verified?
- Which accounts lack an owner?
- Which exceptions are overdue or unassigned?
- Which changes caused disruption and need lessons captured?
Set review frequency according to sensitivity, change rate and organizational requirements. Handle departures and role changes when they happen rather than waiting for the next scheduled review.
A review is not complete when a spreadsheet has approval marks. It is complete when effective access matches decisions, exceptions are controlled and post-change evidence exists.
No comments yet. Be the first to share your thoughts.