
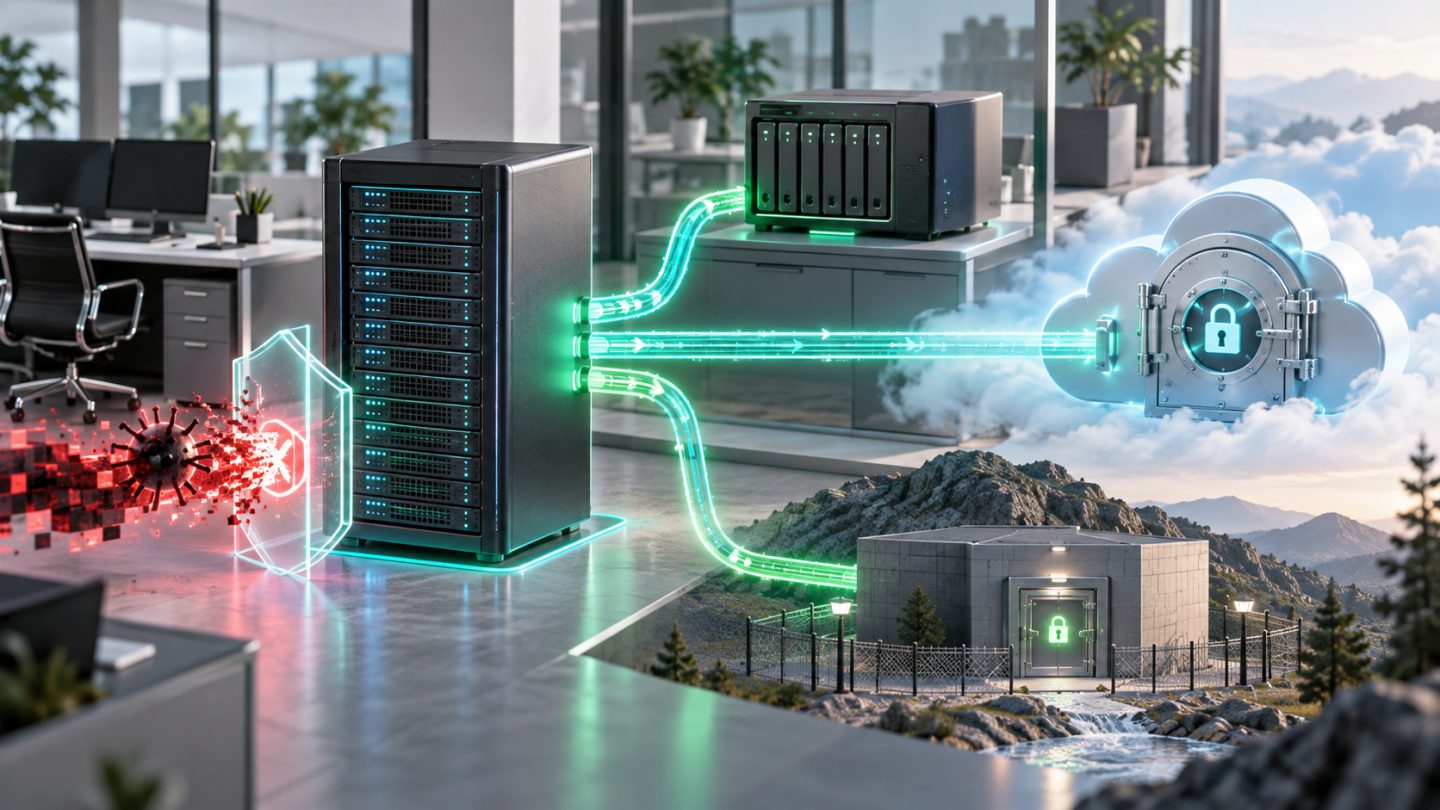
A backup dashboard can report success every night while the recovery team lacks the decryption key or knows too little about application compatibility to restore service. An existing copy is not proof that business operations can resume on time.
This article proposes a small-business recovery drill, from scope to acceptance and follow-up. It is a planning template, not a report of an actual exercise or a universal recovery-time promise.
1. Define success in business terms
Do not stop at “the restore tool finished.” A sales application may need correct sign-in permissions, selected orders, attachments, inventory lookup and a test transaction inside an isolated environment. The business owner should identify the mandatory workflows.
CISA recommends offline encrypted backups and testing backup availability and integrity. CIS Control 11 emphasizes restoration to a trusted state. Turn those principles into a scenario with named owners and verifiable evidence.
2. Agree RPO and RTO before starting the clock
RPO expresses acceptable data loss in time; RTO is the target recovery duration. Agree both with the process owner rather than letting IT choose alone. Define the measurement's starting event and completion criteria, not merely the restore command's runtime.
For illustration, suppose a business tolerates four hours of data loss and expects operations within two hours. If the newest recoverable data predates the incident by six hours, a thirty-minute restore still fails the combined requirements. These are hypothetical numbers, not universal targets.
3. Prepare a one-page drill brief
| Item | Decision required |
|---|---|
| Scope | Application, dataset, recovery point and dependencies |
| Roles | Coordinator, recovery operator, business tester and approver |
| Safety | Isolated network, separate accounts and blocked real-world side effects |
| Acceptance | Business workflows, data freshness, timing and access checks |
| Stop conditions | Production connections, unintended outbound actions or unapproved access |
| Evidence | Timestamps, backup identifier, checks and issue list |
Before the exercise, verify backup access, decryption keys, application build instructions, configuration and dependency versions. Recovery documentation should not exist exclusively inside the system assumed unavailable.
4. Keep the exercise from becoming an incident
Use a separate recovery environment with access controls appropriate to the data. Disable or replace real email, SMS, payment, webhook and synchronization integrations. Inspect workers and schedulers before starting them: copied application configuration may still point to live services.
Do not change public DNS, overwrite live databases or use production-write credentials unnecessarily. If an exercise omits a dependency, document that limit rather than concluding the full service has been proven recoverable.
5. Execute and record each milestone
- The coordinator confirms scope and approval, then starts the agreed clock.
- The operator selects and records the backup and recoverable data point.
- Build the test environment and restore data and application using the runbook, including waiting time.
- Check consistency, associated files, sign-in and authorization.
- A business representative runs agreed workflows with suitable test data.
- Record acceptance time, discrepancies and undocumented actions.
Having to call the only person who remembers a password is itself an important finding. The purpose is to discover weaknesses under controlled conditions, not to produce a flattering report.
6. Produce an actionable conclusion
In a hypothetical drill, technical restoration takes 35 minutes, key-access approval takes another 70 and business checks take 25. The total is 130 minutes against a 120-minute target. Assign an owner to improve key access, set a deadline and retest. More storage capacity would not directly solve that bottleneck.
Afterward, retain evidence in access-controlled storage, handle test data under retention policy and revoke temporary access. Schedule further drills according to criticality, risk and significant application changes. One successful exercise cannot guarantee recovery after every future upgrade.
7. Acceptance checklist
- Recovered data is recent enough for the agreed RPO.
- The complete start-to-acceptance duration is recorded.
- Critical workflows work, not merely database startup.
- Authorization and integrations are safely checked.
- Test limitations are explicit.
- Outstanding issues have owners, deadlines and retests.
A recovery drill turns assumptions into evidence. Start with a manageable scope around one important system, measure the complete process and address bottlenecks before expanding to more complex scenarios.
No comments yet. Be the first to share your thoughts.