
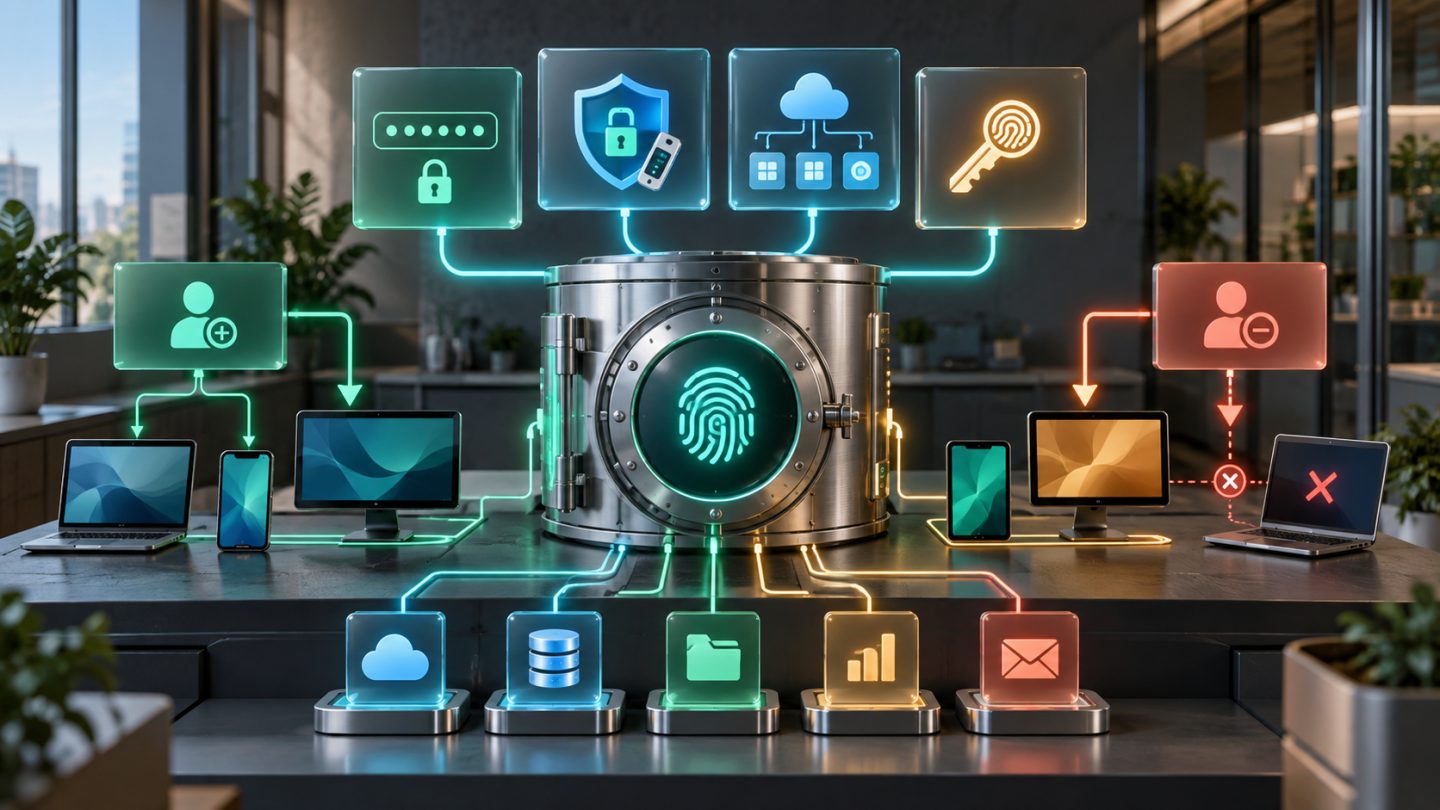
Reusing one password across websites allows an incident at one service to affect other accounts. A password manager makes unique passwords practical without memorizing every credential. Installation is only the beginning: protect the vault and prepare recovery before depending on it.
1. Understand what the vault does
A vault stores credentials so you can use long, random, different passwords. It does not replace device updates, checking website addresses or multi-factor authentication. An infected computer remains a risk even with a password manager installed.
The NCSC buyer's guide recommends considering data protection, software updates, device support and usability. For work accounts, use an organization-approved tool rather than moving company credentials into a personal vault.
2. Configure protection before importing
- Install the application or extension from an official source and verify the publisher.
- If the product uses a master password, choose a long, unique one. Do not reuse your email password or a published example.
- Enable supported multi-factor authentication in line with organizational policy.
- Configure vault auto-lock and enable the device screen lock.
- Understand access from a second device before moving every account.
Distinguish signing into the service from unlocking local vault data. Password, biometric and second-factor requirements differ between products. Do not assume every vault unlock repeats the same authentication steps.
3. Prepare recovery without a circular dependency
Imagine losing your phone while your computer is no longer signed in. Where would you obtain the information needed to open the vault on a new device? If the only recovery material is inside that same locked vault, the plan is incomplete.
Read the provider's documentation on recovery codes, recovery keys or administrative recovery. Not every product can restore data after a forgotten master password. Store recovery material as instructed in a protected location accessible independently, such as a suitably secured paper copy or an IT-approved arrangement.
Review the procedure or use a provider-supported safe checking feature. Do not sign out of every device, delete the vault or disable authentication factors simply to test recovery.
4. Migrate accounts in small groups
The following is a suggested rollout workflow, not a universal product requirement:
- Practice with a low-impact account to learn how entries, website matching and password updates work.
- Once recovery is ready, prioritize primary email and accounts used to recover other services.
- Generate a new password for each service, complete the change on its website and check the corresponding saved entry.
- Test each login before moving on. Keep an existing valid session during checks where the service permits it.
- Continue with work, shopping and remaining accounts according to importance.
Importing an old password does not eliminate reuse. If five websites still share one password, replace it with five different passwords.
5. Treat CSV exports as sensitive material
NCSC notes that some tools export passwords as unencrypted text. Before importing from a browser or another manager, check the export format. Do not send such files through chat or email, or place them in shared synchronization folders.
Prefer a suitable direct transfer or encrypted export when supported. If CSV is necessary, use a trusted device, restrict access, verify the import and handle temporary copies according to security policy. Deleting a file does not prove that copies in the recycle bin, synchronization history or backups are gone.
6. Autofill does not replace checking the website
If the manager offers no credentials on a supposedly familiar login page, pause and inspect the address. Do not immediately copy and paste the password to bypass the inconvenience. The service may have a legitimate new login address, but the page could also be fake.
Open the service from a verified bookmark or official address and check again. HTTPS protects the connection according to that website's certificate; it does not establish that the website belongs to the organization you intended to visit.
7. Everyday readiness checklist
- The vault and device have appropriate locking controls.
- The master password is not used elsewhere.
- An independent, protected recovery path is understood.
- Priority accounts have unique passwords and tested logins.
- Sensitive exports are not left outside your control.
- The master password is not shared, and work accounts follow organizational rules.
The goal is not to collect every secret in one place as quickly as possible. A successful migration reduces password reuse while preserving access when a familiar device or login method is unavailable.
No comments yet. Be the first to share your thoughts.