
Zero Trust is not one product. It is the practice of continuously evaluating users, devices, and context before granting access to resources.
Three principles
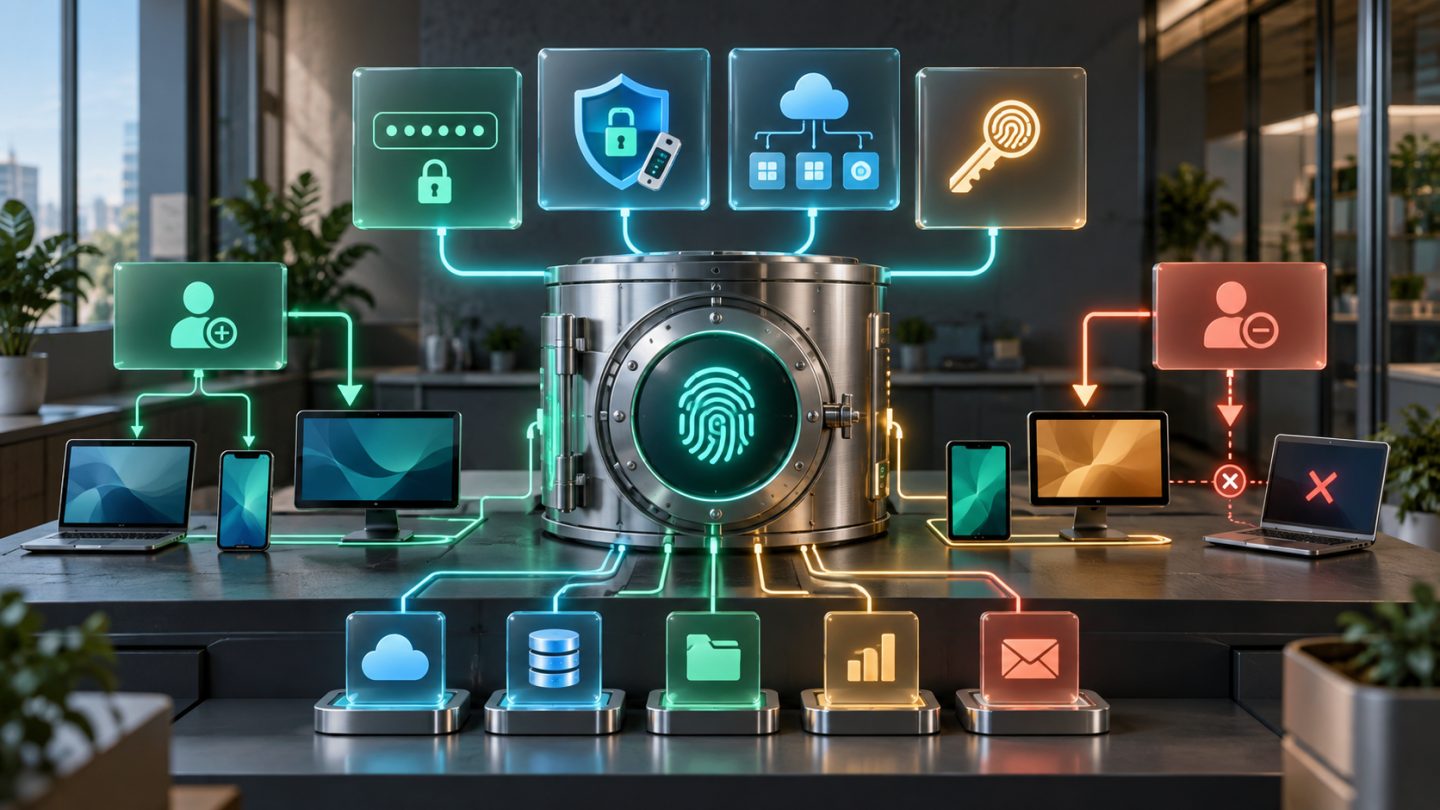
Verify explicitly with multiple signals, grant time-limited least privilege, and assume breach so the potential impact stays contained.
Implementation roadmap
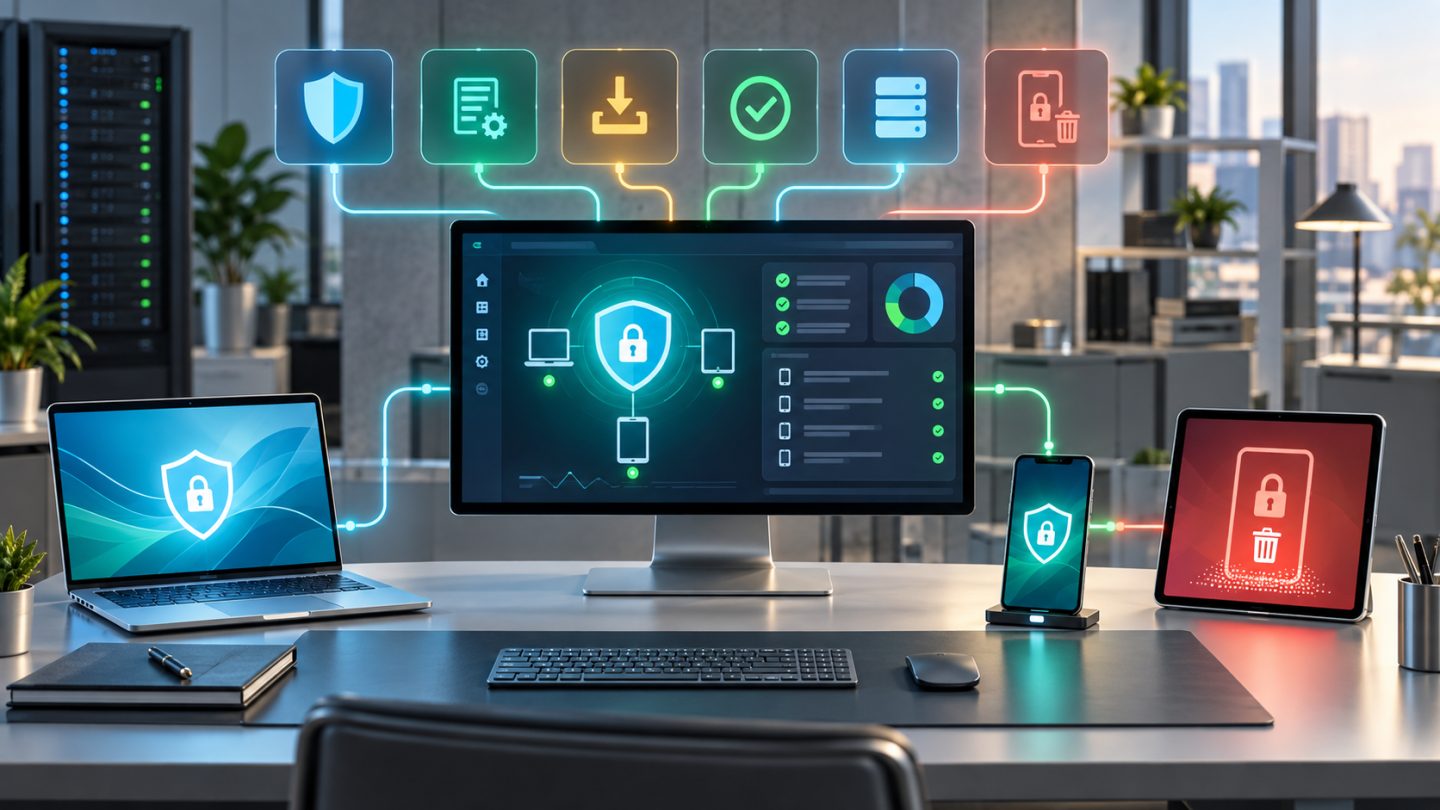
Inventory identities, devices, and data; enable phishing-resistant MFA; standardize updates and encryption; then segment systems, centralize logs, and rehearse access revocation.
Measure progress
Track MFA coverage, managed devices, privileged accounts, revocation time, and applications with centralized logging. Start with administrators, email, VPN, and customer data.
No comments yet. Be the first to share your thoughts.